Mental health professionals carry a heavy documentation and compliance load, and messaging clients outside of sessions adds another layer of risk when it isn’t clearly defined. A quick text or email might feel harmless in the moment, but without a policy in place, staff are left guessing what’s appropriate to send. A clear policy can prevent a misdirected message from becoming a privacy concern for your clients and your practice.
A secure messaging policy for your practice should cover core areas, including what topics are appropriate for messaging and a response plan for privacy breaches. These pieces keep client communications compliant with PIPEDA, regional compliance laws, and your regulatory college’s standards, while providing you with a consistent way to respond when something goes wrong.
1. Your Approved Communication Channels
A secure messaging policy should name the specific tool your practice uses for client communication, whether that’s a client portal, an electronic health record’s built-in messaging system, or another verified, encrypted platform. Naming the exact tool removes ambiguity for staff and prevents them from defaulting to whatever feels most convenient in the moment.
Just as important, state which tools are off-limits. Standard text messaging and general-purpose chat apps typically aren’t built with the encryption and access safeguards a therapy practice needs to protect client information. Spelling this out keeps client information secure because the policy leaves no room for staff to assume a quick text is harmless.
2. What Can and Can’t Be Messaged
Not every message carries the same risk. Your policy should separate administrative communication, such as confirming an appointment time, from clinical or sensitive content, such as treatment details or crisis disclosures. A mental health secure messaging policy keeps high-risk topics, such as detailed assessments or test results, inside a secure portal.
Set clear expectations around urgency, too. State plainly what a client should do in a crisis, such as contacting emergency services or going to the nearest emergency room. Clear instructions here help clients respond quickly in a crisis and give your team confidence in how a message can and can’t be used.
3. Client Consent and Onboarding
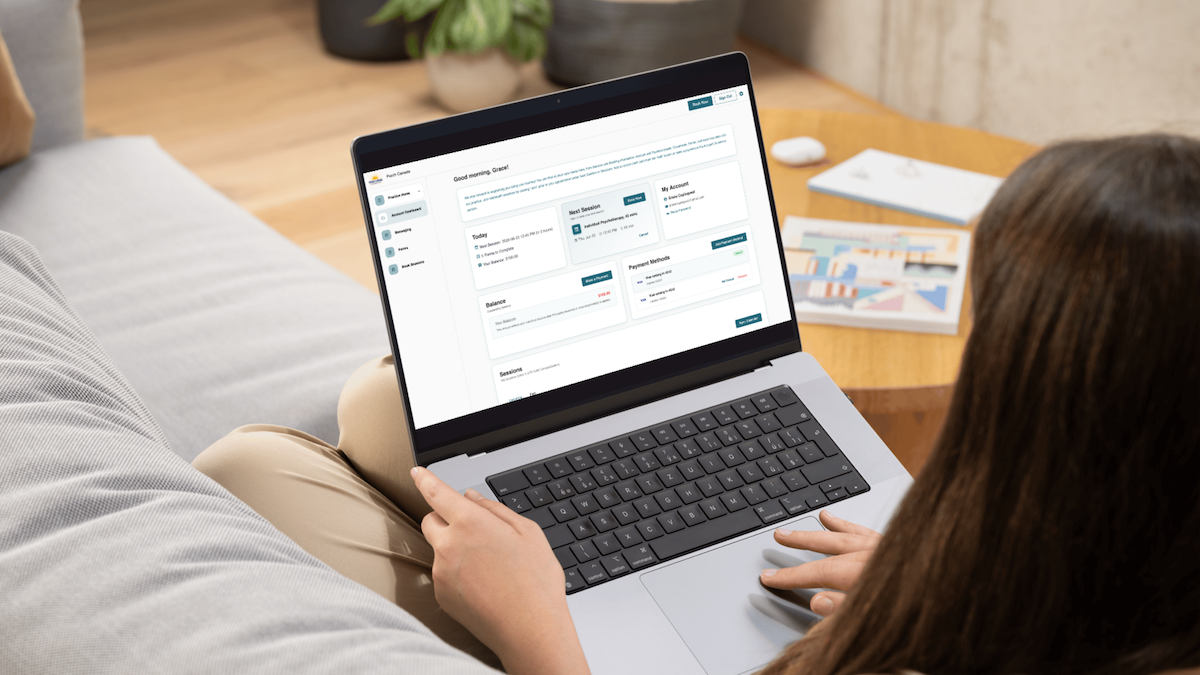
Before a client sends their first message, they should understand the risks and limits of electronic communication, and your practice should document that consent. Your messaging guidelines should explain how clients will receive and access messages. A notification email that omits confidential details and requires logging into a password-protected portal to view the actual content is one way to handle this.
Clients should also know they can withdraw consent for electronic communication at any time. Including this in your policy keeps the relationship transparent and reinforces that messaging is an option you offer.
4. Staff Access, Device, and Training Requirements
Set clear rules for how your team accesses client messages through:
- Approved devices and authentication: Require strong passwords and multi-factor authentication for any account with access to client communication.
- Device restrictions: Restrict staff from using personal phones or unmanaged personal computers to access client messages unless your practice has a specific mobile device management policy.
- Group conversation boundaries: Limit group conversations to a client’s authorized circle of care.
Staff also need to understand the policy for it to work. Build in a short training step whenever a new team member joins or the policy changes, so no one is left guessing how the system is supposed to be used.
5. Documentation and Audit Trail Requirements
Clinically relevant exchanges that occur via messaging should be included in the client’s official record, whether through direct integration, a saved transcript, or a manual note. Keeping these records closes the gap between what you and your client discussed and what’s on file.
Confirm that your messaging platform generates audit logs and define how long you retain conversations in line with your provincial college’s guidelines. A reliable audit trail makes it easier to retrieve a past conversation when you need it.
6. Privacy Breach and Misdirected Message Protocol
Even with strong safeguards, mistakes happen. Your secure messaging policy should outline what to do if a message is sent to the wrong person or a device is lost or compromised, including whom to notify.
Detail how your practice reports a potential privacy incident, both to clients affected and to the appropriate provincial privacy commissioner or the Office of the Privacy Commissioner. Writing this process down before an incident occurs means your team can act quickly and consistently, even under pressure.
Build a Secure Messaging Policy That Works for Your Practice
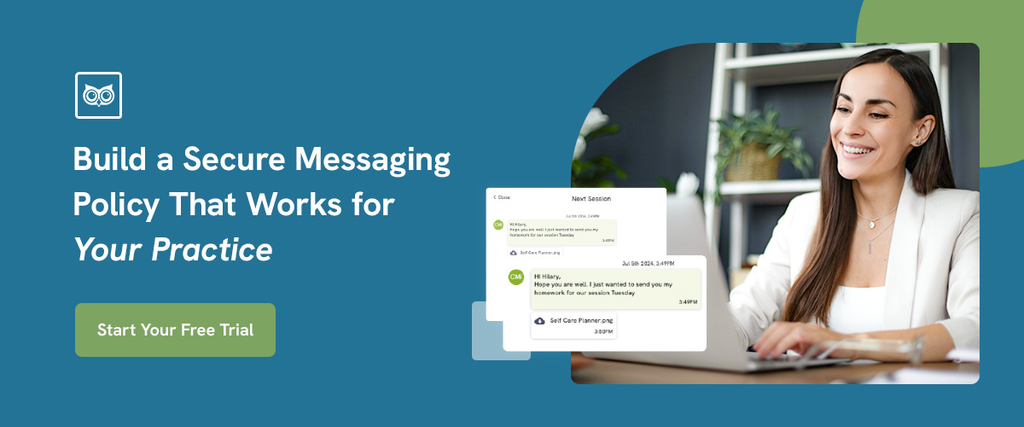
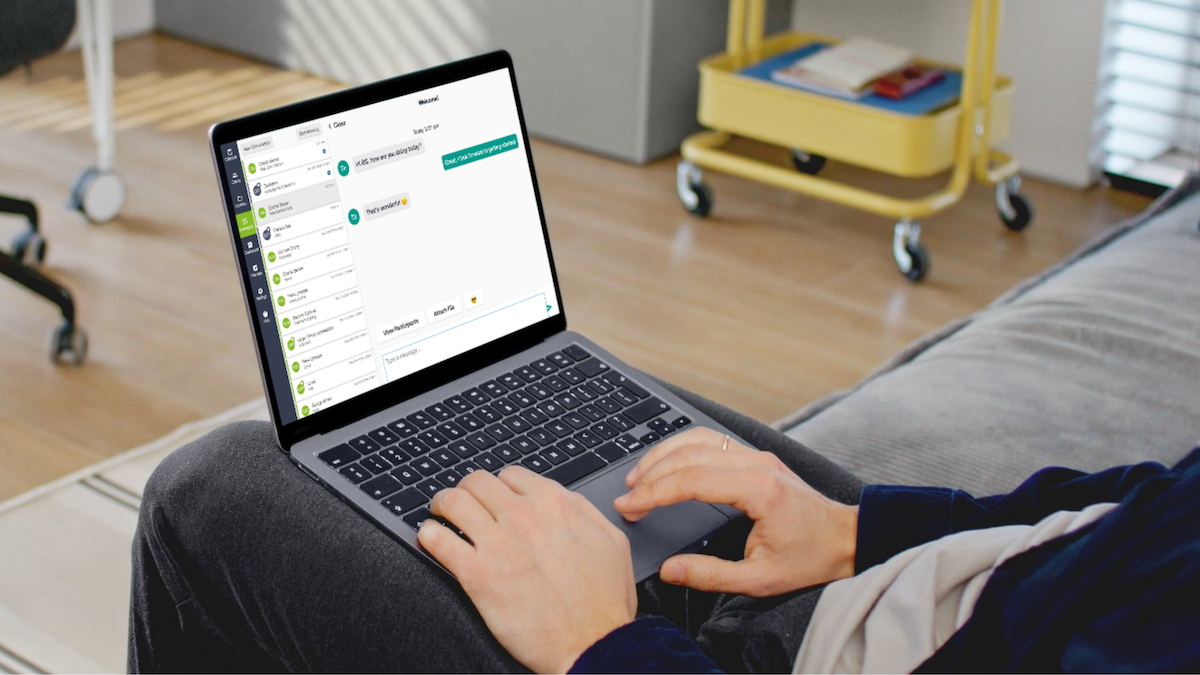
A secure messaging policy helps your practice address unclear processes by providing consistent answers to everyday questions. Owl Practice’s secure messaging feature lets therapists message clients and care teams through a password-protected portal, with each conversation encrypted and automatically documented.
Start your free trial today.